About
AI agents needed IAM. So we built it.
Every AI coding tool, automation, and agent framework asks for the same thing: your API keys. Stripe secret key, GitHub token, Cloudflare credentials — pasted into a .env file, shared across every tool you run, with no way to know what any of them actually touched.
That's the access model most infrastructure had before IAM existed. Cloud providers fixed it for humans and services years ago. Agents never got the same treatment.
Every agent gets a separate identity and permission to retrieve selected service credentials. The runtime receives the configured provider key, so provider scopes remain essential. Credential-access logs show which agent requested which service and when.
What we believe
Least privilege by default
Agents get access to exactly what they need, nothing more.
Approval controls
Require human approval before an agent receives sensitive access.
One audit trail
Every credential access, from every agent, in one place.
Curious how it works under the hood?
Read how we encrypt credentials, apply approval controls, and log every credential request.
Founded by
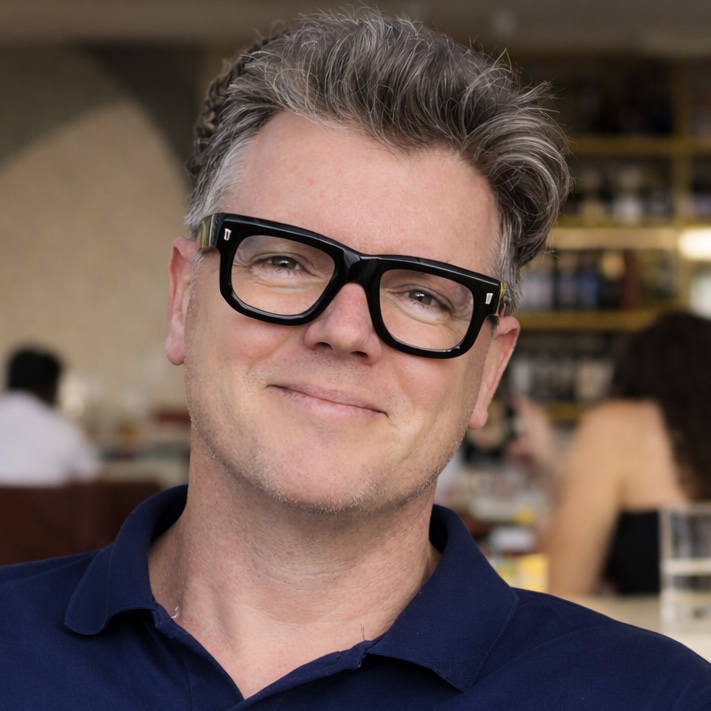
Ash Conway
Founder & CEO
Each service had its own access model — Stripe restricted keys, GitHub token scopes, OpenAI project keys. But when teams started running multiple agents, the per-service controls didn't compose. There was no unified view of which agent held which keys, no cross-service audit trail, no way to cut one agent off without touching every service separately. Ash built Gazebo as the missing layer: a single identity plane for every agent, every service, every access request — scoped credentials, full audit logging, one-click revocation. He founded Bugwolf in 2013 after a decade in enterprise software and hardware — Cisco, SAP, Dell — and bootstrapped it to multimillion-dollar revenue. ashconway.com
Give your agents scoped access
Connect your services once. Every agent gets exactly the credentials it needs.
Get started free